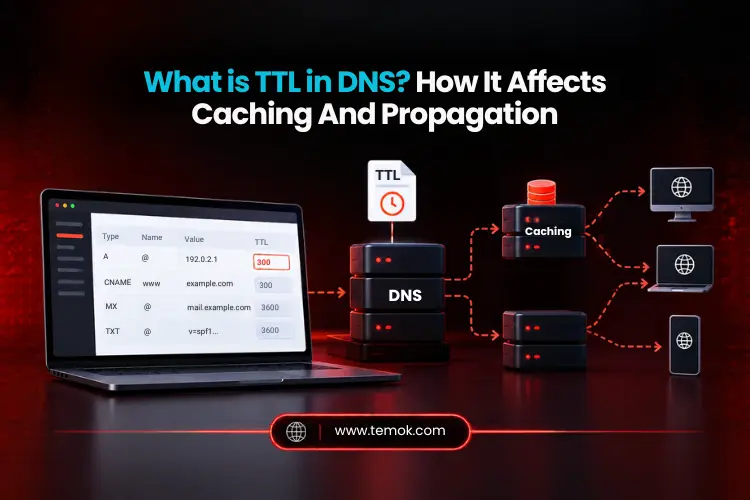
TTL (Time to Live) in DNS tells the resolvers how much time a response from DNS can take to stay cached before asking for fresh information. It is normally measured in seconds.
Imagine you have recently updated a DNS record and yet some of the visitors are still landing on the old server. Isn’t it frustrating, right? The main cause is generally only a number which most of the individuals never check and analyze. This is where understanding what is TTL in DNS becomes more important than ever.
Once you understand this simple TTL meaning in DNS, knowing DNS changes will become much easier to execute and configure. This blog covers exactly what you are looking for because it explains what is DNS TTL, how it works, how it affects caching and propagation, and much more. So, keep reading and exploring to learn more amazing insights about Time to Live DNS.
Key Takeaways
- DNS TTL tells the DNS resolvers how much time a DNS response may take to stay cached. It is measured in seconds.
- A low TTL DNS takes less time to refresh, while a high TTL DNS takes a lot of time and also reduces queries.
- TTL impacts how long old responses stay active after a change. It is not a universal propagation timer.
- TTL values typically range from just one minute to 24 hours, with each reflecting a different level of change.
What is TTL in DNS?
A TTL is an acronym for Time-to-Live. A TTL in DNS represents a value that is measured in seconds and controls how long a DNS resolver can keep a cached response. After that TTL time, the resolver must then ask for updated information.
When the TTL expires, the record itself is not destroyed. Instead, the resolver’s cached copy has reached the end of its authorized duration. The resolver can then request new DNS cache information.
For example, a packet of chips has an expiry date printed on it. However, the date does not destroy the chips in it. Instead, it just tells you when you need to check again before eating. Thus, TTL expiration does not delete the whole DNS record. Understanding what is TTL in DNS becomes important in that case.
How Does DNS TTL Work?
DNS TTL works as a countdown to cached DNS information. A resolver can utilize a cached answer as long as its TTL is valid. Once that period has passed, it needs to collect new information.
The basic DNS TTL working process looks like this:
- A user requests a domain.
- The recursive resolver examines its cache.
- If the cached record is still valid, it will return the cached response.
- The cached TTL begins to count down.
- When the TTL expires, the previously cached response is no longer used as an answer.
- The resolver again asks for updated DNS information.
This basic approach allows DNS to manage a high number of requests without each query reaching the authoritative DNS server.
What Happens When the TTL Expires?
When the TTL (Time-to-Live) expires, the cached answer can no longer be reused. Therefore, the DNS resolver must get fresh information the next time a user requests a domain. However, a DNS record itself stays precisely where it was before.
Moreover, not all resolvers refresh at the same time. For example, a resolver that cached a record 10 minutes ago might have a different remaining TTL than one that cached the exact same record 50 minutes before.
To better understand what TTL is in DNS, you must know how exactly DNS TTL caching works.
How Does DNS TTL Caching Work?
DNS TTL caching works by saving the answers temporarily so the resolvers may use them again over and over. This minimizes the number of repeated DNS requests and can improve lookup efficiency.
For example, if a lot of people request the same domain through a resolver, the resolver may respond from its cache while the record is valid.
As a consequence, the Time to Live DNS value achieves the right balance between keeping information current and preventing needless DNS lookups.
After understanding what is TTL in DNS and how does it work, let’s discuss its importance.
Also Read: What is Private DNS: Easy Configuration For Phones And Laptops
Why is DNS TTL Important?
DNS TTL is important because TTL creates a clear tradeoff between efficiency and freshness. Understanding the tradeoff is critical for both domain owners and network managers. It is also important because it affects how fast changes are identified, how frequently resolvers generate new queries, and how efficiently the DNS info is cached.
TTL in DNS is important because it can affect:
- Cache Efficiency: Query caching decreases the amount of requests made to trusted DNS servers by enabling intermediate DNS servers to remember replies for a certain period of time; the TTL determines how long that period is.
- Record Changes: Shorter Time-to-Lives can assist in making sure that the updated information quickly becomes available.
- Performance Improvement: By caching DNS records, TTL decreases latency for end users, resulting in quicker website loading times.
- DNS Query Volume: A short TTL can cause resolvers to ask for fresh data more frequently.
- Load Reduction: Reduces the demand on authoritative DNS servers by minimizing the number of other repeated inquiries.
- Infrastructure migrations: Lower TTLs can make a scheduled server migration more manageable.
- Failover plans: Shorter TTLs might help when traffic has to be routed to another destination.
The fundamental concept is straightforward: TTL is a trade-off between freshness and caching efficiency. There is no single option that is appropriate for all records. Therefore, understanding what is TTL in DNS deeply is a must for individuals.
Low TTL vs High TTL: What’s the Difference?
A low TTL value makes the cached information expire sooner, while a high TTL value keeps the same information cached for a longer period.
To better understand the difference between low TTL and high TTL, examine the table below:
| Factor | Low TTL | High TTL |
|---|---|---|
| DNS Changes | Refreshed sooner | Cached longer |
| DNS Queries | More frequent | Less frequent |
| Cache Efficiency | Lower | Higher |
| Failover Flexibility | Greater | Lower |
| Suitable For | Changes, migrations, failover | Stable records |
So, neither a lower TTL nor a higher TTL is a better option in every case. Low TTL values offer more flexibility, while high TTL values favor more efficiency.
When Should You Use a Low TTL?
You should use a low TTL when you are expecting a DNS record to update or you need more flexibility during a DNS infrastructure change.
Moreover, you should choose TTL:
- Before planned DNS changes
- During a server migration
- On failover-sensitive records
- On endpoints that change often
When Should You Use a High TTL?
You should use a high TTL when the records rarely change. Since DNS resolvers can keep the response longer, they don’t need to request fresh information as often.
Moreover, you may choose TTL:
- For stable infrastructure
- For records that rarely change
- When efficient caching is the priority
Common DNS TTL Values Explained
Common DNS TTL values range from a minimum of 1 minute to 24 hours or more. The right DNS TTL value relies on how frequently you need to change a record and how fast you need fresh information to be seen.
To better understand what is TTL in DNS settings, look at the table below:
| TTL | Time Equivalent | Typical Interpretation |
|---|---|---|
| 60 | 1 minute | Very short |
| 300 | 5 minutes | Short |
| 1800 | 30 minutes | Moderate |
| 3600 | 1 hour | Common general-purpose value |
| 14400 | 4 hours | Longer caching |
| 86400 | 24 hours | Long caching |
| 604800 | 7 days | Very Long and Uncommon |
DNS TTL 300 (5 minutes) is common and used before migrations since changes appear within five minutes for resolvers that support it. DNS TTL 3600 (1 hour) is a popular everyday option that balances freshness and site caching. However, neither is “the best.” The appropriate value depends on how frequently your records update.
What is the Best TTL For DNS?
There is no single “best” TTL for DNS for every DNS record or domain name. The right TTL value for DNS totally depends on how often the DNS record changes and how fast you need that cached information to expire and fresh updates to appear.
Moreover, consider the following factors for choosing the best TTL for DNS:
- How often the record changes?
- Whether you need rapid failover
- Whether a migration is planned
- How stable your infrastructure is?
- Your query and caching needs
Longer TTLs for stable records can help to reduce duplicate inquiries. Shorter TTLs can help manage changes in records that are likely to change shortly. Meanwhile, DNS TTL settings should be checked whenever infrastructure changes.
Therefore, it is necessary to first understand what TTL in DNS is and what is best.
Does TTL Affect DNS Propagation?
Yes, TTL controls how long an older DNS response can remain in a recursive resolver’s cache after a record changes. However, cache expiration is a more practical concept than a single global DNS propagation timeframe.
DNS updates do not propagate over the internet on a set timer. Instead, each resolver that cached the previous response continues to use it until its remaining TTL expires. That is why DNS TTL propagation differs amongst resolvers.
For example, assume an A record has a TTL of 3600 seconds. A resolver that cached it 10 minutes ago may continue to provide the previous response for around 50 minutes. Furthermore, some resolvers set their own minimum and maximum restrictions, thus actual behavior may differ.
This is why one network may display a fresh DNS record while another maintains the old one. DNS TTL propagation is thus best understood as the result of cached DNS answers expiring at varying intervals.
After learning what TTL in DNS is more deeply, it has become more important for you to understand how you can change the TTL before a DNS migration.
Also Read: Best DNS For Gaming: 8 Fast And Reliable Servers in 2026
How To Change TTL Before a DNS Migration?

The safest option to change TTL before a DNS migration is to lower the TTL, wait for the previous extended cache duration to expire, update the DNS, and then raise the TTL once everything is operating well.
Before the Migration
Before the DNS migration, lower the TTL while the old DNS records are still in an active state.
For example, if your current TTL is 14400, or 4 hours, changing it to 300 seconds (5 minutes) ahead of migration can give newly cached information a much shorter lifetime. Moreover, you should do it before changing the server IP or other critical DNS information.
During the Migration
Once enough time has passed for resolvers with the previous higher TTL to expire, refresh the DNS record. Then, verify the new server to ensure that the domain is reaching the intended destination.
After the Migration
When the new configuration is stable, return the TTL to its regular value. As a consequence, you may recover your caching performance.
Important: Reducing the TTL from 86400 to 300 at the same time as changing the server IP does not cause resolvers to refresh. Resolvers that already have the previous 86400-second response will maintain it till the timeout runs out.
TTL For Different DNS Record Types
TTL applies to all record types, although the appropriate value depends on what each record performs.
Here is what is TTL in DNS for different record types:
A or AAAA Record
As IP address lookups change often, your A records should have a faster TTL. A standard baseline would be about one hour. However, this might be altered according to how frequently adjustments need to be made in an emergency (30 seconds is not unreasonable).
CNAME Record
Typically, your primary website URL, such as www.example.com, should never change. It is recommended that you set your TTL to something longer than the typical session time (which ranges between 2-3 minutes).
MX Record
MX records specify where emails should be delivered. Mail infrastructure is frequently reliable; therefore, using excessively low TTLs may result in more DNS requests with no value.
TXT Record
It is most popular and in use for DKIM records, email security, and domain ownership verification. TXT records are very rarely modified. Thus, any time between 1 and 12 hours should be enough.
Moreover, there is no universal TTL that should be used for every record type, as it depends on what each DNS record does.
How To Check DNS TTL?
You can easily check the current TTL for a DNS response with common command-line tools such as dig and nslookup. The number you get in the answer is the TTL.
To check what is TTL in DNS, use the following alternatives:
1. Check DNS TTL with dig
Run:
dig temok.com
or check an A record by running:
dig A temok.com
In the answer area, you will usually notice a number between the record name and type. That value is the remaining TTL for the response.
For example, the answer will contain a portion that looks like this:
temok.com. 3600 IN A 203.0.113.10
In this case, the TTL is 3600 seconds. It means that this record is cached for only one hour. When a resolver responds from its cache, the TTL value decreases. Querying the authoritative nameserver directly returns the specified value.
2. Check DNS TTL With nslookup
You can also use nslookup to query a domain and retrieve its DNS record. It is very useful for quickly determining whether a resolver is delivering the expected DNS information.
For example, open cmd on Windows and run the following command:
nslookup -debug temok.com
You will get a response like this:

3. Check DNS TTL with Google DNS Checker Tool
You can also check DNS TTL with Google’s free version of DNS checker that is quite lightweight and effective. You just need to enter the domain, and it will provide its TTL for the respective DNS record. Moreover, you can also check the TTL for different records.

DNS TTL Best Practices
Following a few easy DNS TTL best practices will help you plan your DNS updates and avoid complications.
To better understand what is TTL in DNS, follow these DNS TTL best practices:
- Do not utilize exceedingly short TTLs without a good cause.
- When stable records require a longer TTL, use it.
- Reduce the TTL before scheduled migrations.
- Allow the prior TTL ample time to expire before making a crucial update.
- Consider your failover requirements while selecting a TTL.
- When your infrastructure changes, you should review the TTLs.
- Avoid using the same TTL for each DNS record just for convenience.
Frequently Asked Questions (FAQs)
What’s a good TTL for DNS?
There is no single good value. The record determines the ideal TTL. Short numbers, such as 300 seconds, are good for planned modifications, but values of 3600 seconds or more are appropriate for steady records. Therefore, there is no single value for all DNS configurations.
Is a higher or lower TTL better?
Neither “higher TTL” nor “lower TTL” is better. Lowering the TTL will make updates visible more quickly but may result in more DNS lookups. A longer TTL can increase caching, but it can also result in a resolver cache having stale data for a longer period.
What does TTL 1 hour mean?
A TTL of 1 hour means that the DNS response can be cached for a maximum of 3600 seconds before its resolver asks for fresh information. So, when someone asks how long is DNS TTL, the answer will totally depend on the total number assigned to that record.
Why is the TTL value 255?
TTL 255 is often an IP packet TTL, not a DNS TTL. The IP version is an 8-bit hop limit, with a maximum of 255. DNS TTL is a distinct number in seconds.
Conclusion
Understanding what is TTL in DNS is much easier when you see it as a timer for cached DNS data. It does not delete any DNS record. Instead, it specifies the time for which recursive resolvers can use a DNS answer before they query for new data.
Low TTL values can aid with migrations, endpoint changes, and failover strategies. High TTL values are suitable for stable entries and can minimize the number of DNS inquiries.
Most importantly, prepare TTL adjustments before making any big DNS modifications. Lower the TTL early, let earlier cache periods expire, do the necessary updates, then consider increasing the TTL once the new configuration is stable. This straightforward procedure may make DNS transfers smoother and easier to handle.